Paper: 2604.06148 Authors: Andrew Kurtz, Klaudia Krawiecka Categories: cs.CR, cs.AI, cs.MA
The Gap
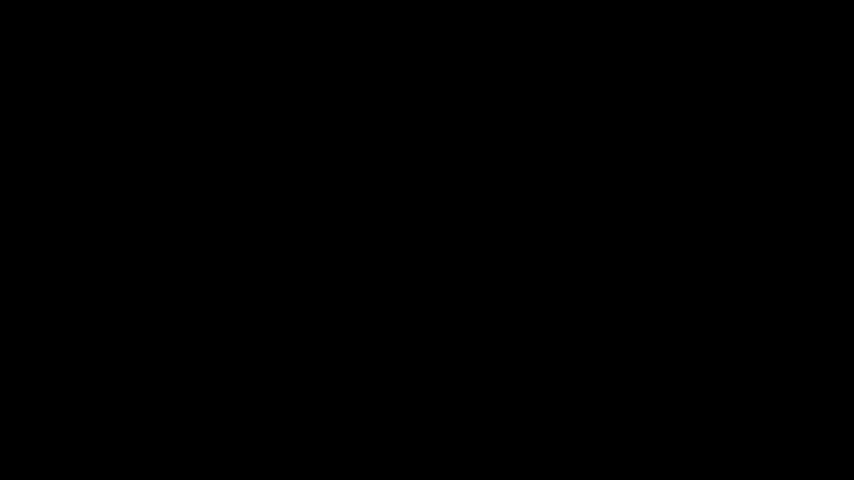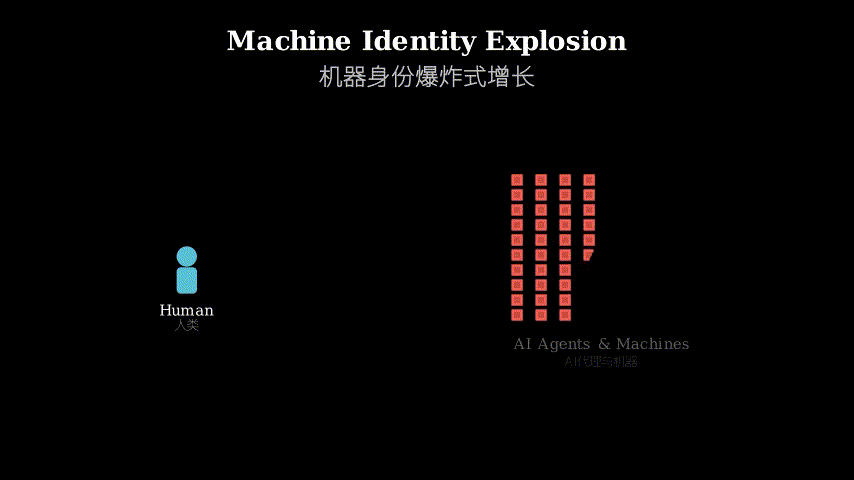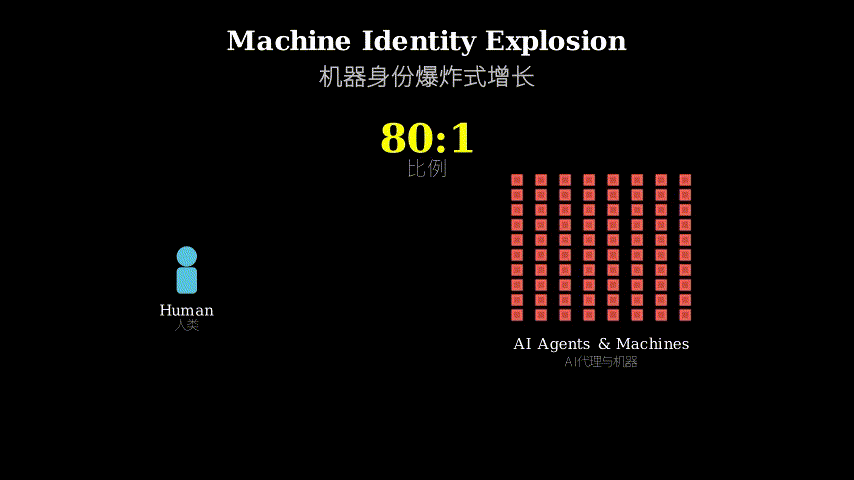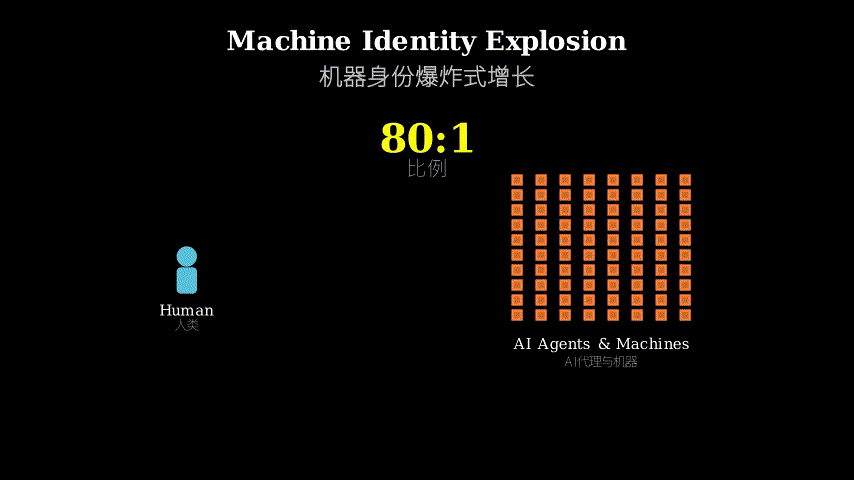
AI governance frameworks focus on model behavior, training data, and human oversight. But they miss the operational layer: the service accounts, API tokens, and automated agents that AI systems use to act in production environments. These machine identities now outnumber human identities 80
in enterprises, yet existing frameworks treat them as infrastructure plumbing rather than governance subjects.The CrowdStrike outage ($5.4-10B in losses) came from one ungoverned automated agent. Nation-state actors (Silk Typhoon, Salt Typhoon) exploit machine credentials as primary attack vectors. Current frameworks address either technical controls (NIST), regulatory compliance (EU AI Act), or geopolitical coordination (UN proposals) — but never all three simultaneously. No taxonomy exists to classify machine identity risks, and no integrated governance model spans technical, legal, and cross-border dimensions.
Problem: AI systems act via ungoverned machine identities
    |
    v
Assumption: Governance requires simultaneous technical + regulatory + geopolitical integration
    |
    v
Method: AIRT (37 risk categories) + MIGT (6-domain framework) + threat model + regulatory mapping
    |
    v
Evidence: Documented incidents, threat intelligence, regulatory analysis, practitioner surveys
    |
    v
Conclusion: Integrated framework enables enterprise implementation across jurisdictions
The Increment
One sentence: Before this paper, machine identity governance was fragmented across technical, compliance, and geopolitical silos; after, enterprises have an integrated taxonomy and framework to govern AI identities across all three dimensions simultaneously.
Core Mechanism
The paper builds two interlocking taxonomies. AIRT (AI-Identity Risk Taxonomy) enumerates 37 specific risk sub-categories across 8 domains: credential lifecycle, privilege escalation, cross-boundary operations, supply chain, adversarial exploitation, regulatory non-compliance, operational resilience, and emergent AI-specific risks. Each risk is grounded in documented incidents (e.g., CrowdStrike outage), threat intelligence (e.g., Silk Typhoon campaigns), regulatory requirements (e.g., EU AI Act Article 15), and practitioner prevalence data.
MIGT (Machine Identity Governance Taxonomy) then provides a six-domain governance framework: technical controls (authentication, authorization, monitoring), organizational structure (roles, responsibilities, escalation paths), regulatory compliance (EU/US/China mapping), cross-jurisdictional coordination (conflict resolution mechanisms), threat modeling (foreign state actor scenarios), and implementation roadmap (four-phase deployment). The framework explicitly addresses conflicts between jurisdictions — for example, EU data localization vs. US cloud sovereignty vs. Chinese cybersecurity law — by providing governance mechanisms rather than pretending conflicts don’t exist.
AIRT (Risk Enumeration)              MIGT (Governance Framework)
        |                                     |
   [37 risks]                          [6 domains]
        |                                     |
        +------> Documented incidents        |
        +------> Threat intelligence         |
        +------> Regulatory requirements     |
        +------> Practitioner data           |
                                              |
                                         [Technical]
                                         [Organizational]
                                         [Regulatory]
                                         [Cross-jurisdictional]
                                         [Threat modeling]
                                         [Implementation]
                                              |
                                              v
                                    Enterprise deployment
Think of this like building a city’s emergency response system. AIRT is the comprehensive hazard map: earthquakes, floods, fires, industrial accidents — each documented with historical incidents, geological surveys, building code violations, and insurance claims. MIGT is the integrated response framework: fire departments (technical controls), city government (organizational structure), building codes (regulatory compliance), mutual aid agreements with neighboring cities (cross-jurisdictional coordination), terrorism scenarios (threat modeling), and the phased rollout plan (implementation roadmap). You can’t respond to a multi-hazard disaster with just a fire department or just building codes — you need all six systems working together, with explicit protocols for when state and federal jurisdictions conflict.
Key Concepts
-
Machine Identity: Not just a credential or token, but the complete operational persona an AI system uses to act autonomously — including authentication mechanisms, authorization scopes, audit trails, lifecycle management, and cross-system trust relationships. A service account running an AI agent isn’t just “a password” — it’s an entity that can spawn child processes, call APIs, access databases, and trigger workflows, often with privileges exceeding any individual human. The CrowdStrike agent had machine identity with kernel-level access across millions of endpoints; when its update logic failed, that identity executed faulty code at scale with no human in the loop.
-
Cross-Jurisdictional Governance Gap: When an AI system operates across EU, US, and Chinese boundaries, it faces irreconcilable legal requirements. EU GDPR demands data localization and right-to-explanation; US CLOUD Act demands law enforcement access regardless of data location; Chinese Cybersecurity Law demands local data storage and government access. Existing frameworks pretend you can “comply with all jurisdictions” — this paper acknowledges conflicts are real and provides governance mechanisms (data sovereignty mapping, jurisdiction-specific identity scopes, conflict escalation protocols) to manage them rather than solve them.
-
Foreign State Actor Threat Model: Traditional identity governance assumes threats are criminals or insiders. But Silk Typhoon (Chinese state actor) and Salt Typhoon (also Chinese) have operationalized machine identity exploitation as primary espionage vectors against critical infrastructure. They don’t steal passwords — they compromise CI/CD pipelines, inject malicious code into automated deployment agents, and use legitimate machine credentials to persist undetected. North Korean actors use AI-enhanced identity fraud to get remote jobs, then use those employee machine identities for espionage. The threat model isn’t “prevent unauthorized access” — it’s “assume machine identities are already compromised by sophisticated state actors with AI capabilities.”
Framework Shift
Before (mainstream approach):        After (this paper):

AI Governance                        AI Governance
    |                                    |
    +-- Model behavior                   +-- Model behavior
    +-- Training data                    +-- Training data
    +-- Human oversight                  +-- Human oversight
                                         +-- Machine Identity Governance
                                              |
Technical controls (NIST)                    +-- Technical (NIST-aligned)
    [separate]                               +-- Organizational
Regulatory (EU AI Act)                       +-- Regulatory (EU/US/China)
    [separate]                               +-- Cross-jurisdictional
Geopolitical (UN proposals)                  +-- Threat modeling (state actors)
    [separate]                               +-- Implementation roadmap
                                              |
[Three silos, no integration]            [Integrated framework]
From fragmented domain-specific controls to integrated governance spanning technical, regulatory, and geopolitical dimensions simultaneously.
Expert Assessment
Problem choice: Real gap, not manufactured. The 80
machine-to-human identity ratio is documented, the CrowdStrike incident is real, and the nation-state threat intelligence is credible. This sits at the intersection of AI governance (hot topic) and identity/access management (mature field) — the insight is recognizing that AI systems’ operational identities are ungoverned, not that AI or identity management are new problems. The timing is right: enterprises are deploying AI agents at scale without governance frameworks.Method maturity: Taxonomy-building rather than algorithmic innovation. The value is in comprehensive enumeration and integration, not clever technique. The 37 risk categories are grounded in real incidents and threat intelligence, which is solid. The six-domain framework is logical but not groundbreaking — it’s essentially “do technical controls AND compliance AND geopolitics together” which is obvious in hindsight but apparently not happening in practice. The cross-jurisdictional conflict acknowledgment is refreshing (most papers pretend conflicts don’t exist), but the resolution mechanisms are high-level governance processes, not technical solutions.
Experimental integrity: No experiments — this is a taxonomy/framework paper. The grounding is in documented incidents, regulatory analysis, threat intelligence reports, and (claimed) practitioner surveys. The CrowdStrike and nation-state actor examples are verifiable. The regulatory mapping appears thorough. The weakness is lack of empirical validation: no case studies of enterprises implementing MIGT, no measurement of risk reduction, no comparison with alternative frameworks. It’s a proposal, not a validated solution.
Writing quality: The paper front-loads impact (CrowdStrike losses, nation-state actors) effectively. The taxonomy structure is clear. But the implementation roadmap is vague — “four-phase deployment” without concrete timelines, resource requirements, or success metrics. The cross-jurisdictional conflict resolution mechanisms are described at governance-process level, not operational detail. The paper would be stronger with one detailed case study showing MIGT implementation and measurable outcomes. The threat model section is solid but could be tighter — some repetition between Silk Typhoon and Salt Typhoon descriptions.
Verdict: weak accept — Addresses a real gap with comprehensive taxonomy and integrated framework, but lacks empirical validation and implementation detail. Valuable for practitioners needing a starting point, but needs follow-up work to prove effectiveness.
Takeaways
For security teams: The 37-category risk taxonomy is immediately usable as a checklist for auditing your AI agent deployments. Specifically, the “credential lifecycle” and “privilege escalation” categories map directly to existing IAM tools — you can start by inventorying service accounts used by AI systems and applying the same lifecycle management (rotation, expiration, least privilege) you use for human identities.
For compliance teams: The EU/US/China regulatory mapping is a practical reference for multi-jurisdictional AI deployments. The key insight: stop trying to “comply with everything” and instead implement jurisdiction-specific identity scopes (EU data stays in EU, accessed by EU-scoped credentials; US data accessed by US-scoped credentials) with explicit governance for cross-boundary operations.
For threat modelers: The foreign state actor scenarios are concrete enough to adapt. The “compromised CI/CD pipeline” and “malicious code injection via automated deployment” scenarios should be added to your threat model if you’re running AI agents in production. The North Korean “AI-enhanced identity fraud for remote employment” scenario is novel and worth gaming out.
For AI governance leads: The core transferable idea is treating machine identities as first-class governance subjects, not infrastructure. If you’re writing AI governance policies, add a section on “operational identity governance” covering authentication, authorization, audit, and lifecycle management for AI agents, service accounts, and API tokens. The framework’s six domains provide a structure for organizing that section.
What’s not transferable: The implementation roadmap is too high-level to execute directly. You’ll need to translate “establish cross-functional governance committee” into actual org charts, meeting cadences, and decision rights for your enterprise.
论文: 2604.06148 作者: Andrew Kurtz, Klaudia Krawiecka 分类: cs.CR, cs.AI, cs.MA
缺口
AI治理框架关注模型行为、训练数据和人类监督。
但它们漏掉了操作层:AI系统在生产环境中用来行动的服务账户、API令牌和自动化代理。
这些机器身份在企业中已经以80:1的比例超过人类身份,但现有框架把它们当作基础设施管道,而非治理对象。
CrowdStrike事故(损失54-100亿美元)源于一个未治理的自动化代理。
国家级行为者(Silk Typhoon、Salt Typhoon)将机器凭证作为主要攻击向量。
当前框架要么处理技术控制(NIST),要么处理监管合规(欧盟AI法案),要么处理地缘政治协调(联合国提案)——但从未同时处理三者。
没有分类体系来归类机器身份风险,也没有整合的治理模型跨越技术、法律和跨境维度。
问题:AI系统通过未治理的机器身份行动
    |
    v
假设:治理需要同时整合技术+监管+地缘政治
    |
    v
方法:AIRT(37个风险类别)+ MIGT(6域框架)+ 威胁模型 + 监管映射
    |
    v
证据:记录的事件、威胁情报、监管分析、从业者调查
    |
    v
结论:整合框架使企业能跨司法管辖区实施
增量
一句话:这篇论文之前,机器身份治理分散在技术、合规和地缘政治孤岛中;之后,企业有了整合的分类体系和框架,可以同时在三个维度治理AI身份。
核心机制
论文构建了两个互锁的分类体系。
AIRT(AI身份风险分类)列举了8个领域的37个具体风险子类别:凭证生命周期、特权升级、跨边界操作、供应链、对抗性利用、监管不合规、运营韧性和新兴AI特定风险。
每个风险都基于记录的事件(如CrowdStrike事故)、威胁情报(如Silk Typhoon活动)、监管要求(如欧盟AI法案第15条)和从业者流行度数据。
MIGT(机器身份治理分类)随后提供六域治理框架:技术控制(认证、授权、监控)、组织结构(角色、责任、升级路径)、监管合规(欧盟/美国/中国映射)、跨司法管辖协调(冲突解决机制)、威胁建模(外国国家行为者场景)和实施路线图(四阶段部署)。
该框架明确处理司法管辖区之间的冲突——例如,欧盟数据本地化 vs 美国云主权 vs 中国网络安全法——通过提供治理机制而非假装冲突不存在。
AIRT(风险枚举)                  MIGT(治理框架)
        |                                |
   [37个风险]                        [6个域]
        |                                |
        +------> 记录的事件              |
        +------> 威胁情报                |
        +------> 监管要求                |
        +------> 从业者数据              |
                                         |
                                    [技术]
                                    [组织]
                                    [监管]
                                    [跨司法管辖]
                                    [威胁建模]
                                    [实施]
                                         |
                                         v
                                   企业部署
把这想象成建设城市应急响应系统。
AIRT是综合灾害地图:地震、洪水、火灾、工业事故——每个都有历史事件、地质调查、建筑规范违规和保险索赔记录。
MIGT是整合响应框架:消防部门(技术控制)、市政府(组织结构)、建筑规范(监管合规)、与邻近城市的互助协议(跨司法管辖协调)、恐怖主义场景(威胁建模)和分阶段推出计划(实施路线图)。
你不能仅用消防部门或仅用建筑规范来应对多灾害灾难——你需要所有六个系统协同工作,并在州和联邦管辖权冲突时有明确的协议。
关键概念
- 机器身份:不仅仅是凭证或令牌,而是AI系统用来自主行动的完整操作角色——包括认证机制、授权范围、审计轨迹、生命周期管理和跨系统信任关系。
运行AI代理的服务账户不只是”一个密码”——它是一个可以生成子进程、调用API、访问数据库和触发工作流的实体,通常拥有超过任何个人的特权。
CrowdStrike代理拥有跨数百万端点的内核级访问权限的机器身份;当其更新逻辑失败时,该身份在没有人工干预的情况下大规模执行了错误代码。
- 跨司法管辖治理缺口:当AI系统跨越欧盟、美国和中国边界运营时,它面临不可调和的法律要求。
欧盟GDPR要求数据本地化和解释权;美国CLOUD法案要求无论数据位置如何都要提供执法访问;中国网络安全法要求本地数据存储和政府访问。
现有框架假装你可以”遵守所有司法管辖区”——本文承认冲突是真实的,并提供治理机制(数据主权映射、特定司法管辖区的身份范围、冲突升级协议)来管理而非解决它们。
- 外国国家行为者威胁模型:传统身份治理假设威胁是罪犯或内部人员。
但Silk Typhoon(中国国家行为者)和Salt Typhoon(也是中国)已将机器身份利用作为针对关键基础设施的主要间谍向量。
他们不窃取密码——他们破坏CI/CD管道,向自动化部署代理注入恶意代码,并使用合法的机器凭证来持久化而不被检测。
朝鲜行为者使用AI增强的身份欺诈来获得远程工作,然后使用这些员工机器身份进行间谍活动。
威胁模型不是”防止未经授权的访问”——而是”假设机器身份已被具有AI能力的复杂国家行为者破坏”。
框架转变
之前(主流方法):                之后(本文方法):

AI治理                            AI治理
    |                                 |
    +-- 模型行为                      +-- 模型行为
    +-- 训练数据                      +-- 训练数据
    +-- 人类监督                      +-- 人类监督
                                      +-- 机器身份治理
                                           |
技术控制(NIST)                          +-- 技术(NIST对齐)
    [分离]                                +-- 组织
监管(欧盟AI法案)                        +-- 监管(欧盟/美国/中国)
    [分离]                                +-- 跨司法管辖
地缘政治(联合国提案)                    +-- 威胁建模(国家行为者)
    [分离]                                +-- 实施路线图
                                           |
[三个孤岛,无整合]                    [整合框架]
从分散的特定领域控制到同时跨越技术、监管和地缘政治维度的整合治理。
专家评审
选题眼光:真实缺口,非人造。
80:1的机器与人类身份比例有记录,CrowdStrike事件是真实的,国家级威胁情报是可信的。
这处于AI治理(热门话题)和身份/访问管理(成熟领域)的交叉点——洞察在于认识到AI系统的操作身份未被治理,而非AI或身份管理是新问题。
时机恰当:企业正在大规模部署AI代理而没有治理框架。
方法成熟度:分类体系构建而非算法创新。
价值在于全面枚举和整合,而非巧妙技术。
37个风险类别基于真实事件和威胁情报,这很扎实。
六域框架合乎逻辑但不具突破性——本质上是”同时做技术控制和合规和地缘政治”,这在事后看来显而易见,但显然在实践中没有发生。
跨司法管辖冲突承认令人耳目一新(大多数论文假装冲突不存在),但解决机制是高层治理流程,而非技术解决方案。
实验诚意:无实验——这是分类体系/框架论文。
基础是记录的事件、监管分析、威胁情报报告和(声称的)从业者调查。
CrowdStrike和国家行为者示例可验证。
监管映射看起来很全面。
弱点是缺乏实证验证:没有企业实施MIGT的案例研究,没有风险降低的测量,没有与替代框架的比较。
这是一个提案,而非经过验证的解决方案。
写作功力:论文有效地前置影响(CrowdStrike损失、国家行为者)。
分类体系结构清晰。
但实施路线图模糊——“四阶段部署”没有具体时间表、资源需求或成功指标。
跨司法管辖冲突解决机制在治理流程层面描述,而非操作细节。
如果有一个详细的案例研究展示MIGT实施和可测量的结果,论文会更强。
威胁模型部分扎实但可以更紧凑——Silk Typhoon和Salt Typhoon描述之间有些重复。
判决:弱接收——用全面的分类体系和整合框架解决真实缺口,但缺乏实证验证和实施细节。
对需要起点的从业者有价值,但需要后续工作来证明有效性。
要点总结
对安全团队:37类风险分类体系可立即用作审计AI代理部署的检查清单。
具体来说,“凭证生命周期”和”特权升级”类别直接映射到现有IAM工具——你可以从清点AI系统使用的服务账户开始,并应用与人类身份相同的生命周期管理(轮换、过期、最小特权)。
对合规团队:欧盟/美国/中国监管映射是多司法管辖区AI部署的实用参考。
关键洞察:停止尝试”遵守一切”,而是实施特定司法管辖区的身份范围(欧盟数据留在欧盟,由欧盟范围凭证访问;美国数据由美国范围凭证访问),并对跨边界操作进行明确治理。
对威胁建模者:外国国家行为者场景足够具体可以改编。
“被破坏的CI/CD管道”和”通过自动化部署的恶意代码注入”场景应添加到你的威胁模型中,如果你在生产中运行AI代理。
朝鲜”AI增强的身份欺诈用于远程就业”场景是新颖的,值得推演。
对AI治理负责人:核心可迁移的想法是将机器身份视为一等治理对象,而非基础设施。
如果你在编写AI治理政策,添加一个关于”操作身份治理”的部分,涵盖AI代理、服务账户和API令牌的认证、授权、审计和生命周期管理。
框架的六个域为组织该部分提供了结构。
不可迁移的:实施路线图过于高层,无法直接执行。
你需要将”建立跨职能治理委员会”转化为你企业的实际组织结构图、会议节奏和决策权。