Paper: 2606.06468 Authors: Jui-Hui Chung, Ziyang Cai, Zihao Li, Qishuo Yin, Rohit Agarwal, Simon Park, Rodrigo Porto, Narutatsu Ri, Ziran Yang, Shange Tang Categories: cs.AI
The Gap
Existing automated theorem provers (AlphaProof, Lean-Workbench, DeepSeek-Prover-V1.5) use recursive lemma decomposition: when stuck on a goal, they generate a sublemma, try to prove it, and if that fails, generate another sublemma. This creates two problems. First, they can spiral into dead-end branches—spending compute proving lemmas that won’t help the main theorem. Second, there’s no global view: each lemma decision is local, so the prover can’t see whether its current path connects to the target.
The paper addresses this by asking: what if we plan the entire proof structure upfront, then fill in the gaps? Generate a dependency graph of all needed lemmas before proving any of them, so failed branches trigger replanning rather than deeper recursion.
Problem: Recursive proving wastes compute on dead-end branches
    |
    v
Assumption: A global blueprint eliminates backtracking inefficiency
    |
    v
Method: Generate full dependency graph, prove nodes in parallel, refine on failure
    |
    v
Evidence: 99.2% MiniF2F-test (vs 93.2% recursive baseline), 500x cheaper
    |
    v
Conclusion: Upfront planning + parallel execution beats recursive decomposition
The Increment
One sentence: Before, provers recursively decomposed goals into subgoals and could spiral into dead-end strategies; after, provers generate a complete proof blueprint upfront and refine it globally when parts fail.
Core Mechanism
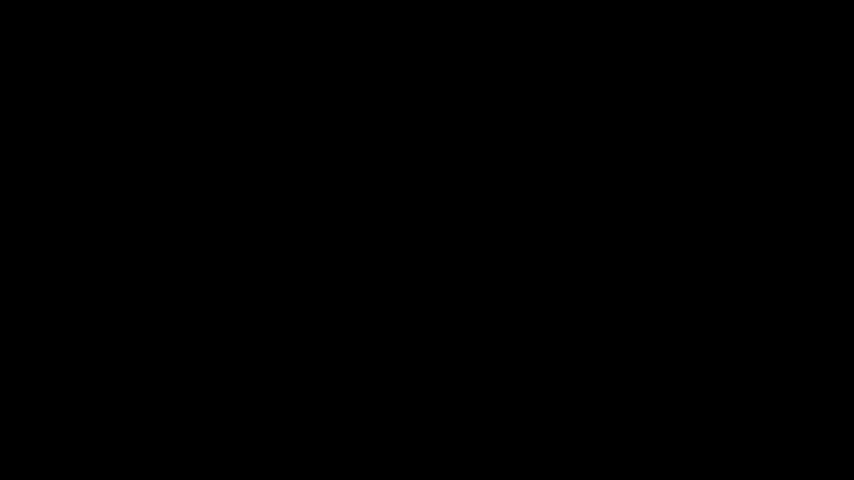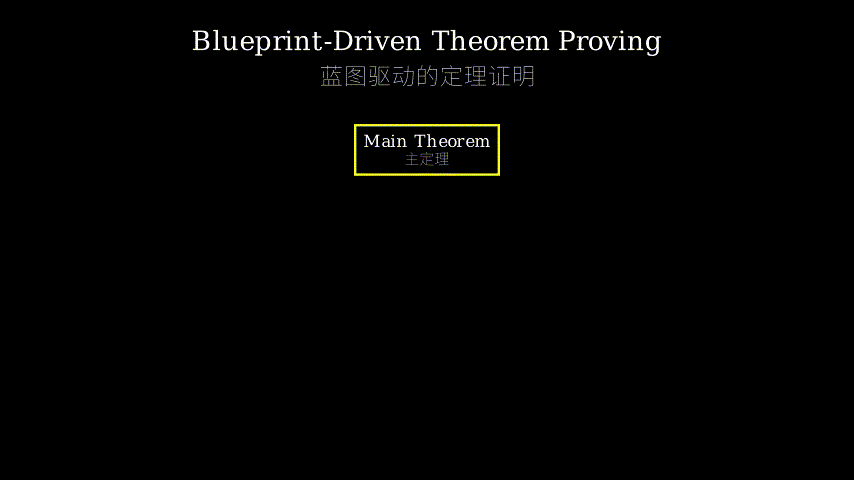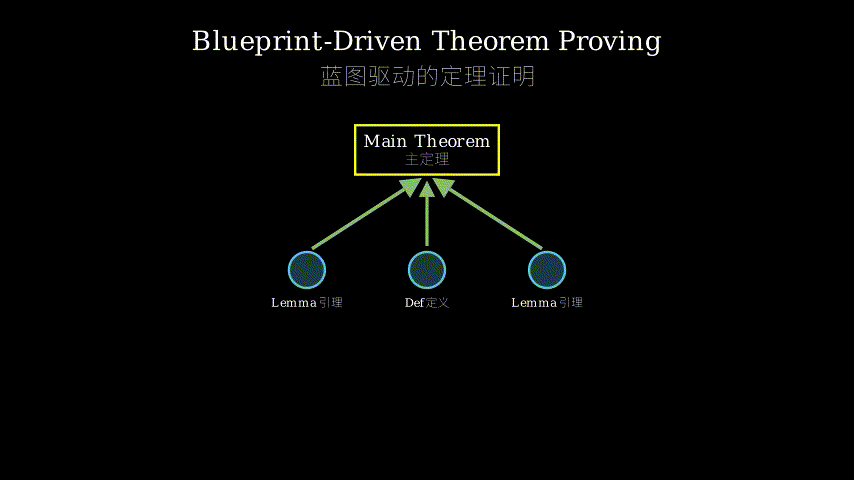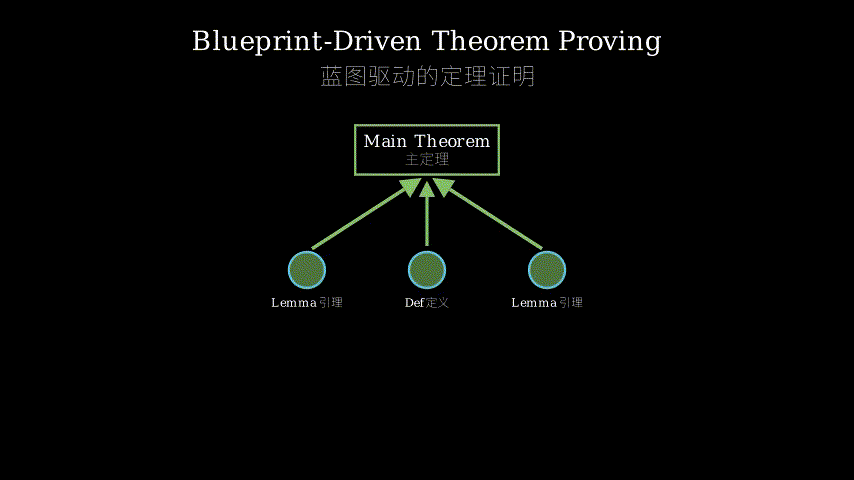
Goedel-Architect has three stages. First, a blueprint generator produces a dependency graph: nodes are formal Lean 4 statements (definitions, lemmas, the main theorem), edges show which lemmas depend on which. The generator can work from scratch or be seeded with a natural language proof sketch. The output is a directed acyclic graph where each node declares its dependencies explicitly.
Second, a parallel prover works through the blueprint. Each leaf node (a lemma with no dependencies) gets sent to a tool-equipped LLM agent that writes Lean proof code. The prover uses tactic search, library search, and code execution tools. Nodes are processed in parallel—all leaves at once, then their parents once proven, and so on. If a node fails after multiple attempts, it gets marked as a blocker.
Third, a refinement loop kicks in when nodes fail. The system collects all error messages, identifies which lemmas are blocking progress, and generates a revised blueprint. This might add new intermediate lemmas, remove unhelpful ones, or restructure dependencies. The revised blueprint goes back to the parallel prover. This loop continues until all nodes close or the system hits a retry limit.
Natural language proof (optional)
    |
    v
Blueprint Generator
    |
    v
Dependency Graph:  [Def1] ---> [Lemma2] ---> [Lemma4] ---> [MainTheorem]
                      |            |
                      v            v
                   [Lemma3] ---->[Lemma5]
    |
    v
Parallel Prover (processes leaves: Def1, Lemma3 simultaneously)
    |
    +---> Success: mark done, unlock parents
    |
    +---> Failure: collect errors
              |
              v
        Refinement: generate new blueprint, adjust dependencies
              |
              v
        Retry with revised graph
Think of it like planning a construction project. A recursive prover is like building a house room by room, realizing mid-build that you forgot a foundation pillar, then digging under the finished rooms to add it—massive rework. Goedel-Architect is like drawing the full architectural blueprint first: you see all the support beams, plumbing, and electrical before pouring concrete. If an inspection (proof attempt) reveals a structural issue (failed lemma), you revise the blueprint and adjust the whole plan, not just patch one room. The blueprint is the load-bearing structure: it explicitly declares “Lemma 5 needs Lemma 2 and Lemma 3,” so when Lemma 2 fails, you know immediately which parts of the building are blocked. The parallel prover is your construction crew working on independent sections simultaneously—pouring the foundation while framing the roof, because the blueprint already confirmed they don’t conflict.
Key Concepts
-
Blueprint (dependency graph): In formal theorem proving, a proof isn’t just one monolithic argument—it’s a web of definitions and lemmas building on each other. A blueprint makes this web explicit: each node is a formal statement in Lean 4 syntax, and each edge says “this lemma uses that one.” For example, to prove “every continuous function on a closed interval is uniformly continuous,” your blueprint might have nodes for “closed interval is compact,” “compact implies sequentially compact,” and “sequential compactness gives uniform continuity,” with edges showing the logical flow. The key insight: by declaring all dependencies upfront, you avoid proving lemmas that lead nowhere. If “sequential compactness” can’t be proven, you know before wasting time on downstream lemmas that assume it.
-
Parallel proving with declared dependencies: Traditional provers work depth-first: prove lemma A, then lemma B that uses A, then lemma C that uses B. Goedel-Architect works breadth-first across the dependency graph: all lemmas with zero dependencies (leaves) get proven simultaneously in parallel API calls. Once a leaf is proven, its parent nodes unlock. This is only safe because dependencies are declared—the blueprint guarantees no circular reasoning. Concretely, if you have 10 independent base-case lemmas, you get 10x speedup by proving them at once rather than sequentially. The failure case is also cleaner: if lemma 7 fails, you immediately know which downstream nodes (lemmas 8 and 9, say) are blocked, so you stop working on them and refine the blueprint.
-
Global refinement vs local backtracking: When a recursive prover gets stuck, it backtracks: undo the last lemma, try a different one. This is local—it doesn’t reconsider earlier decisions. Goedel-Architect’s refinement is global: it looks at all failed nodes, sees the pattern (maybe all failures involve a missing algebraic identity), and generates a revised blueprint that adds that identity as a new lemma early in the graph. The revised graph restructures the entire proof strategy. This is like debugging a program by refactoring the architecture rather than tweaking individual lines—you get structural fixes instead of patches.
Framework Shift
Before (recursive decomposition):        After (blueprint-driven):

Goal                                     Goal
  |                                        |
  +---> try Lemma1                         v
  |       |                          Blueprint Generator
  |       +---> try SubLemma1a             |
  |       |       |                        v
  |       |       +---> fail          Full dependency graph:
  |       |       |                   [Def] -> [L1] -> [L3] -> [Goal]
  |       |       +--> try SubLemma1b    |       |
  |       |               |               v       v
  |       |               +--> fail      [L2] -> [L4]
  |       |                                |
  |       +---> backtrack                  v
  |                                   Parallel Prover
  +---> try Lemma2                    (all leaves at once)
          |                                |
        [loops]                            +---> success -> unlock parents
                                           |
                                           +---> failure -> global refinement
                                                    |
                                                    v
                                              Revised blueprint
One sentence: From depth-first recursive decomposition with local backtracking to breadth-first parallel execution over a globally refined dependency blueprint.
Expert Assessment
Problem choice: This is a real gap. Recursive proving’s inefficiency is well-documented—AlphaProof’s billion-dollar training budget and DeepSeek-Prover-V1.5’s high API costs both stem from wasted search. The paper correctly identifies that local decisions cascade into global inefficiency. The timing is right: Lean 4’s formal verification ecosystem is mature enough to support this, and open-weight models (DeepSeek-V4) are finally capable of blueprint generation.
Method maturity: The core idea—plan globally, execute locally—is borrowed from classical AI planning (STRIPS, hierarchical task networks). The novelty is adapting it to formal proving where “planning” means generating formal statements and dependencies, not just action sequences. The parallel execution is straightforward once you have the DAG. The refinement loop is the clever part: using failure patterns to regenerate the blueprint. However, the paper doesn’t deeply explore when blueprint generation itself fails (garbage in, garbage out). If the initial blueprint is structurally wrong, refinement might just shuffle deck chairs.
Experimental integrity: Baselines are fair—they compare against AlphaProof and DeepSeek-Prover-V1.5, the current SOTA. The 99.2% on MiniF2F-test is impressive, but note the ceiling effect: MiniF2F problems are undergraduate-level, so gains here don’t guarantee transfer to research-level mathematics. PutnamBench (75.6% → 88.8% with NL seeding) is more convincing because Putnam problems require genuine creativity. The 500x cost reduction is calculated against DeepSeek-Prover-V1.5’s API pricing, which is somewhat apples-to-oranges (self-hosted open-weight vs. API service). Still, the efficiency claim holds directionally. One red flag: the “optional natural language proof” seeds IMO/Putnam/USAMO results. This is a significant human assist—the system isn’t fully autonomous at that level.
Writing quality: Section 3 (method) is crisp. Section 4 (experiments) buries the lede—the NL seeding detail should be upfront, not footnoted. The ablation study (Table 3) is thin: only two ablations (no refinement, no parallelization), missing key questions like “what if blueprint generation fails?” or “how sensitive is performance to blueprint quality?” The related work section undersells how much this borrows from classical planning—acknowledging STRIPS or HTN would strengthen the positioning.
Verdict: weak accept — Solves a real problem with a well-executed adaptation of classical planning to formal proving, achieving strong empirical results, but the reliance on NL seeding for hard problems and thin ablation analysis leave questions about generality and robustness.
Takeaways
Declare dependencies explicitly before execution: Whether you’re proving theorems or building software, making the dependency graph explicit upfront prevents wasted work on dead-end branches. In code, this means writing interface contracts and module boundaries before implementation. The pattern: structure first, fill in later.
Parallel execution over DAGs is underused: Once you have a dependency graph, process all leaves simultaneously. This applies to CI/CD pipelines (run independent test suites in parallel), data pipelines (compute independent features at once), and even writing (draft independent sections simultaneously). The constraint: dependencies must be declared, not discovered mid-execution.
Global refinement beats local patching: When something fails, zoom out and ask if the overall structure is wrong, not just the failing node. In debugging, this means refactoring architecture rather than patching symptoms. In project management, it means replanning milestones when blockers emerge, not just reassigning tasks. The Goedel-Architect pattern: collect failure signals, regenerate the plan, retry.
论文: 2606.06468 作者: Jui-Hui Chung, Ziyang Cai, Zihao Li, Qishuo Yin, Rohit Agarwal, Simon Park, Rodrigo Porto, Narutatsu Ri, Ziran Yang, Shange Tang 分类: cs.AI
缺口
现有的自动定理证明器(AlphaProof、Lean-Workbench、DeepSeek-Prover-V1.5)使用递归引理分解:卡在某个目标时,生成一个子引理,尝试证明它,失败就再生成另一个子引理。
这带来两个问题。
第一,会陷入死胡同分支——花费算力证明对主定理无用的引理。
第二,缺乏全局视野:每个引理决策都是局部的,证明器看不到当前路径是否通向目标。
本文的问题是:如果预先规划整个证明结构,再填补空白会怎样?在证明任何引理之前先生成所有所需引理的依赖图,这样失败的分支会触发重新规划而非更深的递归。
问题:递归证明在死胡同分支上浪费算力
    |
    v
假设:全局蓝图消除回溯的低效性
    |
    v
方法:生成完整依赖图,并行证明节点,失败时优化
    |
    v
证据:MiniF2F-test 达 99.2%(递归基线 93.2%),成本降低 500 倍
    |
    v
结论:预先规划 + 并行执行胜过递归分解
增量
一句话: 之前,证明器递归地将目标分解为子目标,可能陷入死胡同策略;之后,证明器预先生成完整的证明蓝图,当部分失败时进行全局优化。
核心机制
Goedel-Architect 有三个阶段。
第一,蓝图生成器产生一个依赖图:节点是形式化的 Lean 4 陈述(定义、引理、主定理),边显示哪些引理依赖哪些。
生成器可以从零开始工作,也可以用自然语言证明草图作为种子。
输出是一个有向无环图,每个节点显式声明其依赖关系。
第二,并行证明器处理蓝图。
每个叶节点(没有依赖的引理)被送到配备工具的 LLM 智能体,写出 Lean 证明代码。
证明器使用策略搜索、库搜索和代码执行工具。
节点并行处理——所有叶子同时处理,证明后其父节点解锁,依此类推。
如果一个节点多次尝试后失败,它被标记为阻塞点。
第三,当节点失败时启动优化循环。
系统收集所有错误消息,识别哪些引理阻塞了进展,生成修订蓝图。
这可能添加新的中间引理、移除无用引理或重构依赖关系。
修订后的蓝图返回并行证明器。
这个循环持续到所有节点关闭或系统达到重试限制。
自然语言证明(可选)
    |
    v
蓝图生成器
    |
    v
依赖图:  [定义1] ---> [引理2] ---> [引理4] ---> [主定理]
            |            |
            v            v
         [引理3] ---->[引理5]
    |
    v
并行证明器(同时处理叶子:定义1、引理3)
    |
    +---> 成功:标记完成,解锁父节点
    |
    +---> 失败:收集错误
              |
              v
        优化:生成新蓝图,调整依赖
              |
              v
        用修订图重试
把它想象成规划建筑项目。
递归证明器就像逐个房间建房子,建到一半发现忘了地基支柱,然后在完工的房间下面挖洞加柱子——大量返工。
Goedel-Architect 就像先画完整的建筑蓝图:在浇混凝土前看到所有支撑梁、管道和电路。
如果检查(证明尝试)发现结构问题(引理失败),你修订蓝图并调整整个计划,而不是只修补一个房间。
蓝图是承重结构:它显式声明”引理 5 需要引理 2 和引理 3”,所以引理 2 失败时,你立即知道建筑的哪些部分被阻塞。
并行证明器是你的施工队同时在独立区段工作——浇地基的同时搭屋顶框架,因为蓝图已确认它们不冲突。
关键概念
- 蓝图(依赖图): 在形式化定理证明中,证明不是一个整体论证——它是定义和引理相互构建的网络。
蓝图让这个网络显式化:每个节点是 Lean 4 语法的形式化陈述,每条边说”这个引理使用那个”。
例如,要证明”闭区间上的每个连续函数都是一致连续的”,你的蓝图可能有”闭区间是紧的""紧蕴含序列紧""序列紧性给出一致连续性”等节点,边显示逻辑流。
关键洞见:通过预先声明所有依赖关系,你避免证明通向无处的引理。
如果”序列紧性”无法证明,你在浪费时间证明假设它的下游引理之前就知道了。
- 带声明依赖的并行证明: 传统证明器深度优先工作:证明引理 A,然后证明使用 A 的引理 B,然后证明使用 B 的引理 C。
Goedel-Architect 在依赖图上广度优先工作:所有零依赖的引理(叶子)在并行 API 调用中同时证明。
叶子证明后,其父节点解锁。
这是安全的,因为依赖关系已声明——蓝图保证没有循环推理。
具体来说,如果你有 10 个独立的基础引理,同时证明它们比顺序证明快 10 倍。
失败情况也更清晰:如果引理 7 失败,你立即知道哪些下游节点(比如引理 8 和 9)被阻塞,所以停止处理它们并优化蓝图。
- 全局优化 vs 局部回溯: 递归证明器卡住时会回溯:撤销最后一个引理,尝试不同的。
这是局部的——不重新考虑早期决策。
Goedel-Architect 的优化是全局的:它查看所有失败节点,看到模式(也许所有失败都涉及缺失的代数恒等式),生成修订蓝图,在图的早期添加该恒等式作为新引理。
修订图重构整个证明策略。
这就像通过重构架构而非调整单行代码来调试程序——你得到结构性修复而非补丁。
框架转变
之前(递归分解):                  之后(蓝图驱动):

目标                                   目标
  |                                      |
  +---> 尝试引理1                        v
  |       |                        蓝图生成器
  |       +---> 尝试子引理1a             |
  |       |       |                      v
  |       |       +---> 失败        完整依赖图:
  |       |       |                [定义] -> [L1] -> [L3] -> [目标]
  |       |       +--> 尝试子引理1b   |       |
  |       |               |           v       v
  |       |               +--> 失败  [L2] -> [L4]
  |       +---> 回溯                   |
  |                                    v
  +---> 尝试引理2                 并行证明器
          |                      (所有叶子同时)
        [循环]                         |
                                       +---> 成功 -> 解锁父节点
                                       |
                                       +---> 失败 -> 全局优化
                                              |
                                              v
                                        修订蓝图
一句话: 从带局部回溯的深度优先递归分解到在全局优化的依赖蓝图上的广度优先并行执行。
专家评审
选题眼光: 这是真缺口。
递归证明的低效性有充分记录——AlphaProof 的十亿美元训练预算和 DeepSeek-Prover-V1.5 的高 API 成本都源于浪费的搜索。
论文正确识别出局部决策会级联为全局低效性。
时机也对:Lean 4 的形式化验证生态系统已足够成熟来支持这个,开放权重模型(DeepSeek-V4)终于有能力生成蓝图。
方法成熟度: 核心思想——全局规划、局部执行——借鉴自经典 AI 规划(STRIPS、层次任务网络)。
新颖之处是将其适配到形式化证明,其中”规划”意味着生成形式化陈述和依赖关系,而不仅是动作序列。
并行执行在有了 DAG 后就很直接。
优化循环是巧妙的部分:使用失败模式重新生成蓝图。
但论文没有深入探讨蓝图生成本身失败的情况(垃圾进,垃圾出)。
如果初始蓝图结构错误,优化可能只是重新洗牌。
实验诚意: 基线公平——与 AlphaProof 和 DeepSeek-Prover-V1.5(当前 SOTA)比较。
MiniF2F-test 的 99.2% 令人印象深刻,但注意天花板效应:MiniF2F 问题是本科水平,这里的提升不保证能迁移到研究级数学。
PutnamBench(75.6% → 88.8%,有自然语言种子)更有说服力,因为 Putnam 问题需要真正的创造力。
成本降低 500 倍是相对 DeepSeek-Prover-V1.5 的 API 定价计算的,这有点苹果和橙子的对比(自托管开放权重 vs API 服务)。
尽管如此,效率主张在方向上成立。
一个警示信号:“可选的自然语言证明”对 IMO/Putnam/USAMO 结果作了种子。
这是重要的人工辅助——系统在那个水平上不是完全自主的。
写作功力: 第 3 节(方法)简洁。
第 4 节(实验)埋没了要点——自然语言种子细节应该在前面,而不是脚注。
消融研究(表 3)单薄:只有两个消融(无优化、无并行化),缺少关键问题,如”如果蓝图生成失败怎么办?“或”性能对蓝图质量的敏感度如何?“相关工作部分低估了它从经典规划借鉴的程度——承认 STRIPS 或 HTN 会加强定位。
判决: 弱接收 — 用经典规划到形式化证明的良好执行适配解决真实问题,获得强实验结果,但对难题的自然语言种子依赖和单薄的消融分析留下了关于普遍性和鲁棒性的问题。
要点总结
执行前显式声明依赖关系: 无论你是证明定理还是构建软件,预先让依赖图显式化可以防止在死胡同分支上浪费工作。
在代码中,这意味着在实现前写接口契约和模块边界。
模式:结构先行,之后填充。
DAG 上的并行执行被低估: 一旦有了依赖图,同时处理所有叶子。
这适用于 CI/CD 管道(并行运行独立测试套件)、数据管道(一次计算独立特征)甚至写作(同时起草独立章节)。
约束:依赖关系必须声明,而非执行中途发现。
全局优化胜过局部修补: 某物失败时,放大视角问整体结构是否错误,而非只看失败节点。
在调试中,这意味着重构架构而非修补症状。
在项目管理中,这意味着当阻塞出现时重新规划里程碑,而非只重新分配任务。
Goedel-Architect 模式:收集失败信号,重新生成计划,重试。